Ver categorias
Explorar
Fiverr Pro
Português
$
USD
Strategic SOC Services Advisor
Are you collecting threat intelligence data without turning it into actionable intelligence your SOC can act on?
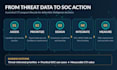
I assess and develop Cyber Threat Intelligence (CTI) programmes that align business risks, intelligence requirements, threat analysis, and security operations. With over 20 years of cybersecurity experience across SOC, CTI, incident response, and threat hunting, I provide practical, vendor-neutral advisory services.
Depending on your package, you receive:
Deliverables include executive-ready reports and, where appropriate, editable work products.
This is a documentation-led advisory service, not live monitoring or platform deployment. Message me on Fiverr to confirm scope before ordering.

Which package should I choose?
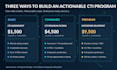
Basic helps understand current CTI maturity and identify gaps. Standard designs a structured CTI programme with governance, requirements, and operational workflows. Premium adds enterprise integration planning, expanded scope, and executive advisory services.
Can you build a CTI program from scratch?
Yes. Standard and Premium can design a new CTI operating model, including its governance, intelligence requirements, processes, deliverables, and implementation roadmap. Actual deployment is a separately scoped activity.
What documents do you need?
Relevant CTI or SOC policies, existing threat intelligence procedures, available security tool information, organisational objectives, and previous assessments are helpful. Sanitised documents are preferred.
Is my information confidential, and can you sign an NDA?
Yes. I can review and sign a mutually acceptable Non-Disclosure Agreement before any confidential documents are exchanged. We will agree on appropriate information-handling arrangements and limit the information collected to what the engagement requires.
Do you need access to our production systems?
No direct access to production is required for the assessment and design packages. The engagement focuses on evidence review, stakeholder discussions, operating-model documentation, and integration requirements.
Which frameworks do you support?
Depending on the agreed scope, I can consider NIST CSF 2.0, ISO/IEC 27001, MITRE ATT&CK, and relevant sector-specific threat intelligence principles. Formal certification or compliance attestation is not included.
Do you provide CTI platform implementation or ongoing monitoring?
The published packages cover CTI assessment, programme development, and integration planning. Live deployment, threat-feed subscriptions, and managed monitoring are separate services.
Can you customize the scope?
Yes. Additional business units, stakeholder interviews, intelligence requirements, workflows, and system integrations can be included as agreed extras or via a custom Fiverr offer.
What counts as a revision?
Revisions cover the clarification and refinement of agreed deliverables. New workstreams, additional technical scope, and extra workshops are treated as additional services.


