Ver categorias
Português
$
USD
Conecte-se à sua IA
Cybersecurity Services, VAPT, SOC, Cloud Security, GRC, Brand Protection
Is your Microsoft Sentinel flooding your team with false alerts, or missing real attacks? We build and tune Sentinel so your SOC sees what matters.
What you get:
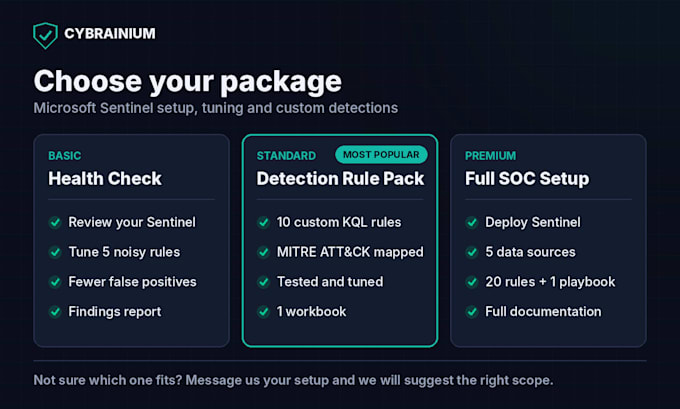
- Sentinel deployment and log source onboarding
- Custom KQL detection rules mapped to MITRE ATT&CK
- Tuning of noisy rules to cut false positives
- Workbooks and dashboards for your team
- Automated response playbooks with Logic Apps
- Clear documentation and handover
Why work with us:
- 7+ years in SOC, detection engineering and incident response
- SC-200, CEH and Splunk certified
- Every rule is tested with sample attack data before delivery
How it works:
1. Share your setup: data sources, licenses and current rules
2. We confirm scope and timeline before you order
3. We build, test and deliver with a walkthrough
Not sure which package fits? Send us your setup and we will suggest the right scope.
Note: we only work on environments you own or are authorized to manage. We will need Reader or Contributor access to your Sentinel workspace.

Provedor de nuvem:
microsoft azure
Recurso de computação em nuvem:
Grupos de Segurança
•
Outros
What access do you need to my environment?
Reader access is enough for a health check. For building rules and playbooks we need Microsoft Sentinel Contributor on your workspace. You can remove access as soon as the work is delivered.
Can you tune our existing rules instead of building new ones?
Yes. The Basic package is built for this. We review your current analytics rules, find the noisiest ones and tune them to cut false positives without losing real detections.
Do you work with Splunk or other SIEMs?
Yes. We also build detections in Splunk, and we can migrate rules from Splunk or another SIEM to Microsoft Sentinel using the Migration extra.
How do you keep our data confidential?
We only access what the task needs, never copy your logs outside your environment, and are happy to sign your NDA before starting.
Do you offer ongoing support after delivery?
Yes. We offer monthly detection tuning and new rule development. Message us and we will send a custom offer based on your environment.